See Your Blast Radius Before Attackers Do
Ghost Mode walks your cloud the way a real adversary would — tracing every exposure, identity and permission from the public internet to your crown jewels.
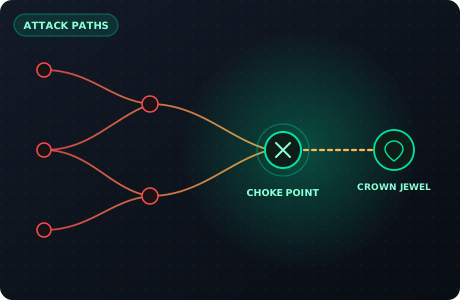
What Attack Path Analysis gives you
Ghost Mode walks your cloud the way a real adversary would — tracing every exposure, identity and permission from the public internet to your crown jewels.
Real paths, not flat lists
See the exact routes from internet exposure to crown jewels — every hop, identity and permission in between.
IAM escalation detection
Ghost Mode reasons about privilege escalation and role assumption chains that static scanners miss entirely.
Choke-point remediation (Closed-Loop)
Arkhein identifies and severs the highest-leverage paths by generating automated Pull Requests with AST and Checkov validation, atomically closing findings in the graph.
Multi-cloud reachability
Paths are traced across AWS, Azure, GCP, OCI and Huawei Cloud on a single graph — including cross-account and cross-cloud movement.
More than a list of findings
Attestable validation
Puppet Master can safely emulate a path end-to-end to prove it is genuinely exploitable — no more guessing.
AI impact narratives
The Cyber AI Analyst explains, in plain language, what each path means for the business and how to close it.
Who it's for
Cloud security & CNAPP teams, Security engineers & architects, Red & purple teams, CISOs & security leadership
Answers about
Attack Paths
Most cloud security tools hand you a list of thousands of findings with no sense of which ones an attacker could actually chain together. Arkhein's Attack Path Analysis takes the opposite approach: it walks your cloud the way a real adversary would, following every exposure, identity and permission from the public internet to your most sensitive assets.
Ghost Mode combines deterministic graph traversal over your live cloud map with an AI layer that reasons about IAM escalation, lateral movement and misconfiguration chains. Instead of a flat severity score, you get the actual routes to your crown jewels — ranked by how reachable and how damaging they are — across AWS, Azure, GCP, OCI and Huawei Cloud.
Because every path is grounded in the same graph that powers posture, identity and compliance, remediation is precise: Arkhein highlights the choke points that break the most paths at once, and generates closed-loop Pull Requests to eliminate them.
Yes. What-If Simulation applies a proposed change — closing a port, removing a node or revoking a permission — to a copy of the graph and shows which attack paths disappear, without touching your environment.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.