See Every Permission, Every Identity, Every Risk
Map every entitlement across your multi-cloud environment — and find the overprivileged identities that create real attack paths.
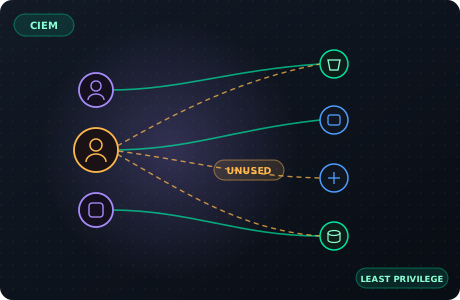
What CIEM gives you
Map every entitlement across your multi-cloud environment — and find the overprivileged identities that create real attack paths.
Entitlement mapping
Every permission for every identity across AWS, Azure, GCP and OCI — visible and searchable.
Graph-contextualized risk
Overprivileged identities ranked by real reachability — not just permission count.
Unused permission detection
Find permissions that have never been used and can be safely revoked.
Least-privilege recommendations
AI-powered suggestions for the minimum permissions each identity actually needs.
More than a list of findings
Cross-cloud identity view
See all identities and their permissions across all clouds in one place.
Just-in-time access
Recommendations for time-bound, scoped access instead of standing privileges.
Who it's for
Identity & access management teams, Cloud security engineers, DevSecOps teams, Compliance & audit teams
Answers about
CIEM
Cloud permissions are complex. A single IAM policy can contain hundreds of permissions, and most organizations have thousands of identities across multiple clouds. Arkhein's CIEM engine maps every entitlement to every identity, then correlates that data with the attack graph to find the permissions that actually matter.
Traditional CIEM tools list permissions. Arkhein contextualizes them. An overprivileged service account is only a risk if it can reach sensitive resources — and Arkhein's graph knows exactly what it can reach. Permission findings are ranked by real exploitability, not just theoretical risk.
The CIEM module also powers just-in-time access recommendations — suggesting the minimum permissions needed for each identity based on actual usage patterns, and flagging permissions that have never been used.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.