Cloud Security Posture Management
Continuously audit your multi-cloud configuration against CIS, NIST, PCI-DSS and custom frameworks — with findings mapped to the exact resources that matter.
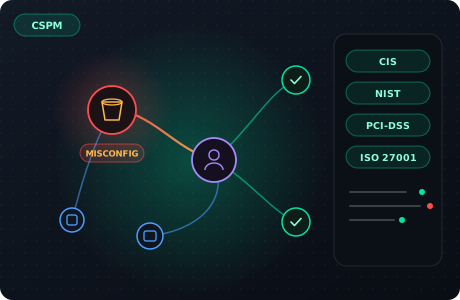
What CSPM gives you
Continuously audit your multi-cloud configuration against CIS, NIST, PCI-DSS and custom frameworks — with findings mapped to the exact resources that matter.
Multi-cloud coverage
AWS, Azure, GCP and OCI audited under a single pane of glass — no per-cloud dashboards.
Graph-connected findings
Every misconfiguration is placed in context: which resources it touches, what it enables, and how it chains with other risks.
Regulatory framework mapping
Automatic mapping to CIS, NIST, BACEN 4893, LGPD, PCI-DSS, SOC2, ISO 27001 — with compliance reports exportable to PDF.
Continuous monitoring
Scans run on a schedule you define, with instant alerts when a new misconfiguration appears or a configuration drifts from baseline.
More than a list of findings
Remediation guidance
Every finding includes a prioritized remediation step — often a one-click fix via infrastructure-as-code patch.
Custom policies
Write your own security policies in a simple DSL and enforce them across all clouds from one place.
Who it's for
Cloud security engineers, DevSecOps teams, Compliance & audit teams, CISOs & security leadership, Platform engineering teams
Answers about
CSPM
Traditional CSPM tools flood teams with thousands of disconnected findings. Arkhein takes a different approach: every misconfiguration is mapped onto your live cloud graph, showing exactly which resources are affected, how they connect to other risks, and what an attacker could chain together.
Powered by Prowler and our proprietary Go scanner, Arkhein ingests your AWS, OCI, GCP and Azure configurations in real time and evaluates them against CIS Benchmarks, regulatory frameworks (BACEN 4893, LGPD, PCI-DSS 4.0, SOC2, ISO 27001) and your own custom policies.
Findings are not just listed — they are prioritized by real exposure. A publicly accessible S3 bucket connected to an overprivileged IAM role ranks higher than the same bucket in isolation, because Arkhein understands the graph.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.