Cloud-Native SIEM With Context
Detect threats across your multi-cloud environment with findings enriched by graph context — not just log signatures.
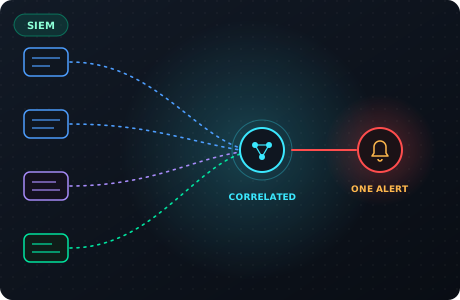
What SIEM / CDR gives you
Detect threats across your multi-cloud environment with findings enriched by graph context — not just log signatures.
Multi-cloud log ingestion
CloudTrail, Azure Activity Log, GCP Audit Log, OCI Audit — all ingested and normalized in real time.
Graph-enriched alerts
Every alert is contextualized with the affected resource, connected findings, and potential blast radius.
Behavioral anomaly detection
UEBA-powered baseline learns normal behavior and flags deviations — compromised credentials, unusual API patterns, privilege escalation.
Threat correlation
Cross-reference events across clouds to detect coordinated attacks that single-cloud SIEMs miss.
More than a list of findings
Guided response
Every detection includes remediation guidance and links to the exact controls that were violated.
Custom detection rules
Write your own detection logic and enforce it across all clouds from one place.
Who it's for
SOC analysts, Threat detection engineers, Incident responders, Cloud security teams
Answers about
SIEM / CDR
Traditional SIEMs generate thousands of alerts with no context. Arkhein's Cloud Detection & Response (CDR) pipeline correlates cloud logs, configuration changes, and behavioral signals with the live security graph — so every alert comes with context about what is affected, how it connects to other risks, and what the blast radius would be.
Arkhein ingests CloudTrail (AWS), Activity Log (Azure), Audit Log (GCP), and OCI Audit events in real time. Each event is mapped to the graph resource it affects, cross-referenced with existing findings, and scored for severity based on real exposure — not just CVSS.
When a threat is detected, Arkhein does not just send an alert — it provides the full context: which resource is affected, what attack paths it enables, and which controls are violated. Response is guided, not guessed.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.