Detect Anomalies Before They Become Incidents
User and Entity Behavior Analytics that learns what normal looks like in your cloud — and flags deviations the moment they appear.
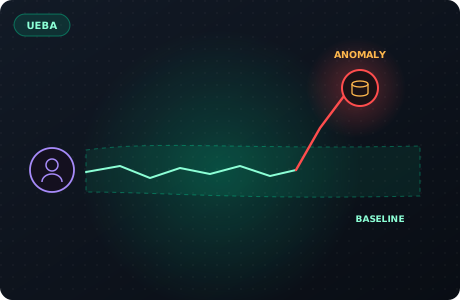
What UEBA gives you
User and Entity Behavior Analytics that learns what normal looks like in your cloud — and flags deviations the moment they appear.
Behavioral baselines
Learn normal patterns for every user, service account, and entity across all clouds.
Graph-aware anomaly detection
Detect deviations based on what was accessed, not just what was called.
Compromised credential detection
Flag credential misuse, impossible travel, and unusual API patterns.
Confidence scoring
Every anomaly comes with a confidence score and behavioral timeline.
More than a list of findings
SIEM integration
Feed behavioral context into the CDR pipeline for enriched detection.
Custom baselines
Define entity-specific baselines for critical service accounts and admin users.
Who it's for
SOC analysts, Threat detection engineers, Identity & access management teams, Incident responders
Answers about
UEBA
Signature-based detection misses novel attacks. Arkhein's UEBA engine builds a behavioral baseline for every user, service account, and entity in your cloud — then flags deviations that indicate compromise, misuse, or misconfiguration.
The baseline is graph-aware. It understands not just what an entity did, but what it accessed, what permissions it used, and what resources it touched. A service account that suddenly enumerates S3 buckets it has never touched before is flagged — even if each individual API call is technically permitted.
UEBA integrates with the SIEM/CDR pipeline, enriching every detection with behavioral context. This means alerts come with a confidence score, a behavioral timeline, and a clear explanation of why the activity is anomalous.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.