Agentic Shield.
AI agents read your data, run commands and call APIs. Know which ones exist, and bound what they can do.
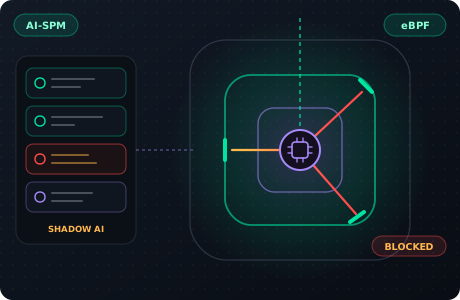
Find every agent, bound every action
Agents act with real credentials. Agentic Shield starts with an inventory and ends with policy at the kernel.
AI-SPM
Inventory models, agents, vector stores and MCP servers across your accounts.
Shadow AI
Find the AI nobody registered, before it finds your data.
Agentic Kernel
Kernel-level visibility into what an agent process reads and sends.
Agentic Kernel Firewall
Policy for local coding agents and MCP servers: which files, which commands, which destinations.
AI with guardrails you can audit
Exfiltration Enclave
Exfiltration needs a place to be stopped. Kernel-level visibility into what an agent reads and sends gives it one.
Least privilege for agents
The Agentic Kernel Firewall decides which files, commands and destinations each local agent or MCP server may use.
Limits: enforcement depends on supported OS and kernel versions.
Shadow AI, found
Agents and MCP servers that nobody registered show up in the same inventory as the ones you approved.
LLM Guardrails & Audit
For Arkhein's own AI: redaction before any model call, quotas, an audit log and a disclosure of what the AI used on every answer.
Answers about
Agentic Shield
Models, agents, vector stores and MCP servers across your connected accounts.
AI services and agents running in your accounts that nobody registered or approved.
The Agentic Kernel Firewall applies policy on which files, commands and destinations an agent may use. Enforcement depends on supported OS and kernel versions.
No. Your data is not used for training. It is only cross-referenced between Arkhein features, for example graph, ledger and findings.
Redaction before any model call, quotas, an audit log and a disclosure of what the AI used on every answer.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.