Container & Kubernetes.
Image CVE scanning and Kubernetes posture across EKS, AKS, GKE and OKE — connected back to the workloads they actually run on.
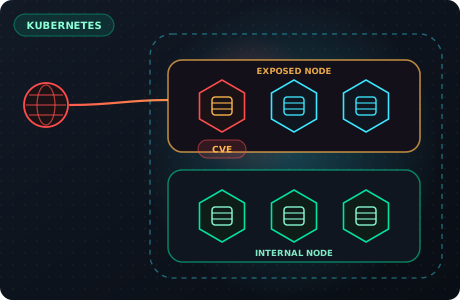
From cluster to the CVE that matters
Clusters, namespaces, pods and the images they run join the same graph as your cloud accounts, so a container vulnerability is judged by what it can reach.
Cluster inventory
Clusters, namespaces and the pods running in EKS, AKS, GKE and OKE are collected into Arkhein.
Into the Hyper-Graph
Each pod is linked to its namespace, its cluster and the worker node that hosts it.
Image CVEs
Every running image is scanned and its vulnerabilities are attached to the image in the graph.
Exposure first
A vulnerable pod on a worker reachable from the internet ranks above the same image on an internal node.
Fix what is actually running
Running images, not just the registry
Findings come from the images your pods run, so the list matches what is deployed.
Blast radius from the node
Pods are connected to the worker nodes that host them, so a compromised node shows which workloads are at stake.
Limits: exposure is inferred from the worker node's network settings.
One graph with your cloud
Cluster findings sit on the same Hyper-Graph as identities, networks and data, so a container CVE becomes part of the attack path to your crown jewels.
Explore the Hyper-GraphFits your plan
Kubernetes nodes count towards your plan, and Container & Kubernetes Security can be added in Build Your Plan.
See plans
Answers about
containers and Kubernetes
EKS, AKS, GKE and OKE.
The focus is the images your pods run, so the findings match what is actually deployed.
By exposure: a vulnerable image on a pod whose worker node is reachable from the internet ranks above the same image on an internal node.
In the Kubernetes view of the Arkhein platform: clusters, namespaces and pods with the vulnerabilities of their images.
Kubernetes nodes count towards your plan limits, and the module can be added in Build Your Plan.
Ready to see your cloud
as an attacker does?
Book a demo and our team will walk you through Arkhein on your own cloud.